Security
HIPAA compliant med spa software
AEVA is HIPAA compliant. AEVA signs a Business Associate Agreement (BAA) with every customer at sign-up.
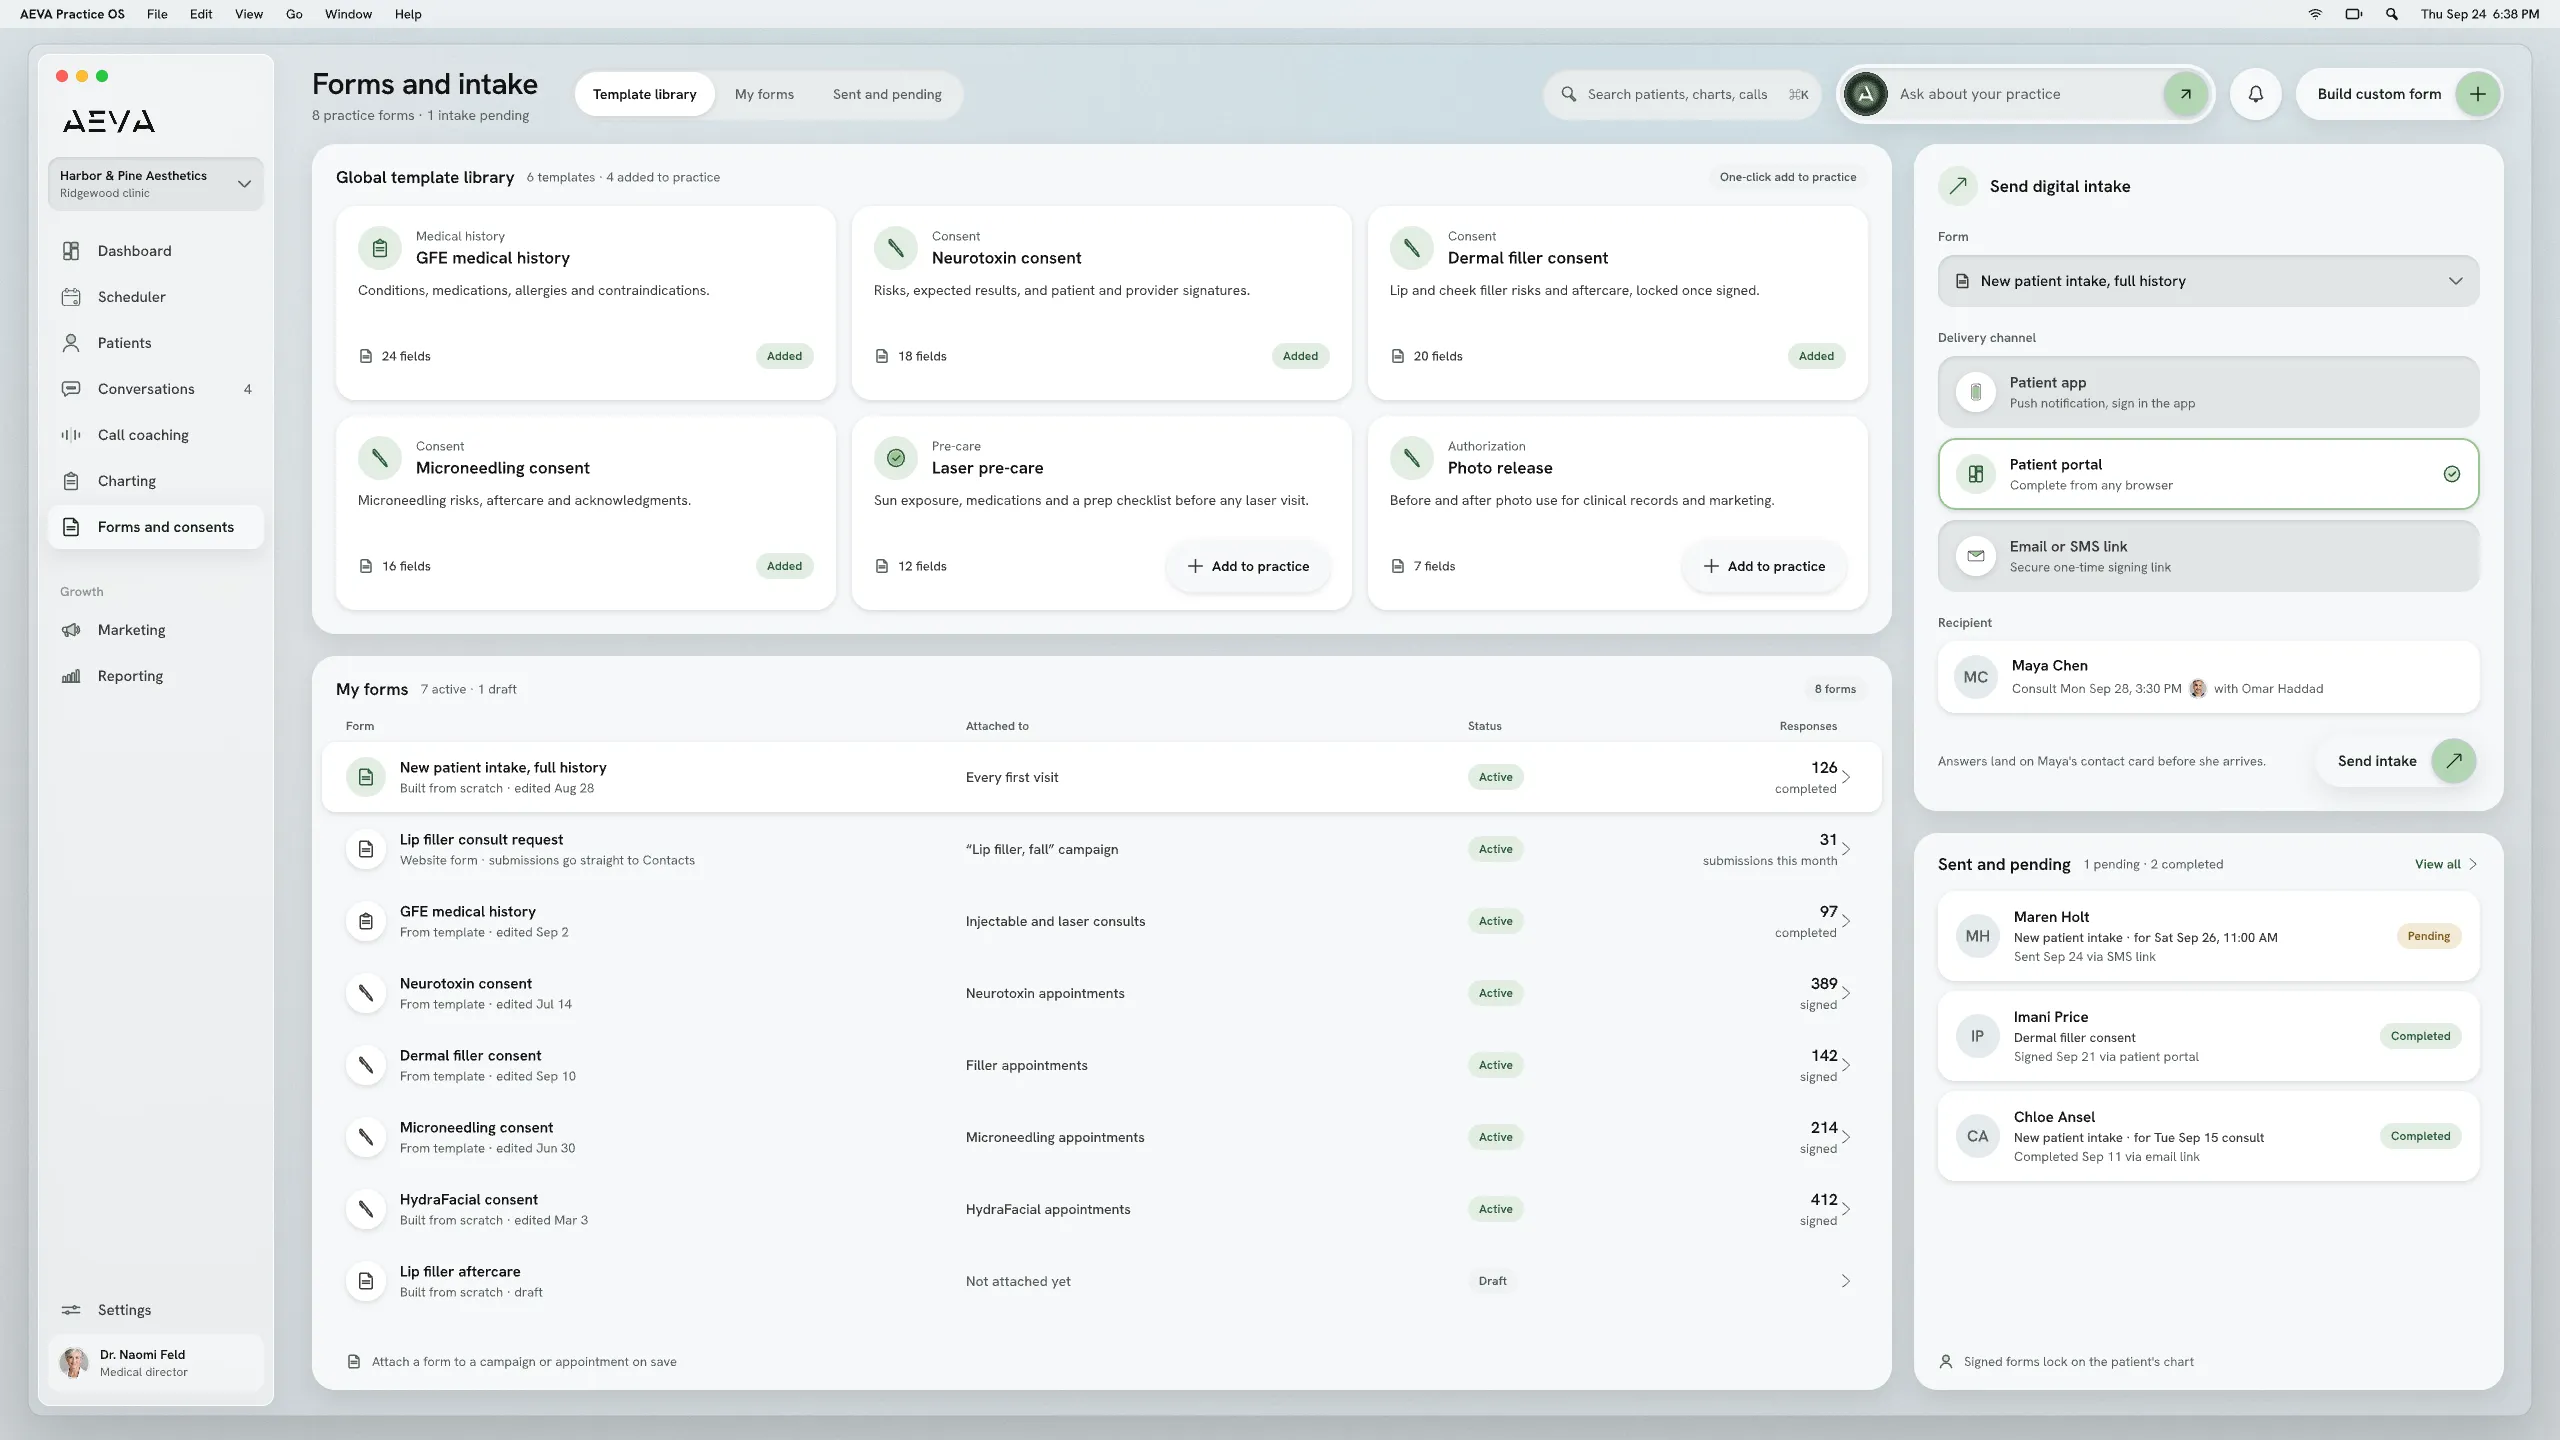
Practice OS, forms and intake. Demo data.
-
Growth Engine
Marketing on the same data
Every Growth Engine plan includes Practice OS.
-
Practice OS
Where your patient data lives
CRM, scheduling, charting and payments share the same data.
HIPAA
HIPAA compliant, in plain words
HIPAA has no official certificate, so here's what we do and what we won't claim.
What we do
For every customer
- AEVA is HIPAA compliant.
- AEVA never uses patient data to train AI models.
- Role-based permissions across your whole team.
- Two-factor authentication options, on the public scheduler too.
No official certificate
What to ask for instead
- That's why we say HIPAA compliant and show no badge.
- The signed BAA is the document you can hold us to.
- Ask any vendor that handles patient data for one too.
The BAA
A signed BAA from day one
AEVA signs a Business Associate Agreement (BAA) with every customer at sign-up.
Book a demoYour BAA
Signed at sign-up- What a BAA is The contract HIPAA requires before a vendor handles your patients' data.
- Signed when you start It's part of sign-up, with nothing extra to request.
- Signed on every plan Every customer gets one, whatever the plan or the practice size. On every plan
AI training
No training on patient data
Access and sign-in
Permissions and two-step sign-in
Roles set what each person can reach, and two-factor options guard sign-in.
-
Role-based permissions
Role-based permissions across the team set what each person can see and change.
Your front desk and your providers can have different access, set by role.
-
Two-factor authentication
Two-factor authentication options add a second check after the password.
Those options reach the public scheduler too, where patients book online.
-
A profile per person
Every team member gets a profile with role-based permissions of their own.
Separate toggles set who shows on the calendar and on the public scheduler.
-
Consent forms that lock
Send consent forms, HIPAA consent included, through the patient app or portal.
Both sides sign, then the form locks so the signed record can't be altered.
Key facts
Products
Practice OS andGrowth Engine.
Founded 2021
-
Patient data
AEVA never uses patient data to train AI models.
-
Security
AEVA is HIPAA compliant.AEVA signs a Business Associate Agreement (BAA) with every customer at sign-up.
-
Team access
Role-based permissions across the team, plus two-factor authentication options.
-
AI assistants
AEVA grants MCP access on request, within each user's permissions.
-
Your expert
Every practice works directly with an AEVA expert, whatever the plan.
-
Contact
sales@aevadigital.com1-833-4-MYAEVA
FAQ
Security questions
Short answers on HIPAA, the BAA, AI training and who can see patient records.
Is AEVA's med spa software HIPAA compliant?
Yes. AEVA is HIPAA compliant. AEVA signs a Business Associate Agreement (BAA) with every customer at sign-up. That goes for med spas and every other practice we work with.
See what Practice OS doesDo I have to ask for a BAA?
No. AEVA signs a Business Associate Agreement (BAA) with every customer at sign-up. It comes with getting started on any plan, so there's nothing extra to request.
Does patient data train AEVA's AI?
No. AEVA never uses patient data to train AI models. That covers charts, consent forms, messages and call recordings, and you don't have to switch anything off.
How to remove your ad platform dataWho certifies HIPAA compliance?
No government agency does, so no official certificate exists. Ask any vendor that holds patient data for its BAA, the contract you can hold it to.
Who on my team can see patient records?
Inside your practice, role-based permissions across the team set what each person can see. Two-factor authentication options add a second check at sign-in.
Bring your security questions to a demo
AEVA is HIPAA compliant. Book a demo to learn more about our BAA, AI training, team access, etc.
Book a demo